Most software bugs are irritating. They freeze apps, wipe unsaved work, or crash screens at the worst possible moment. Yet some errors escape the confines of computers and wreak havoc across hospitals, rockets, power grids, financial systems, and even human lives, highlighting the wide-ranging impact of software failures.
These disasters reveal the hidden dangers of blindly trusting machines. A minor miscalculation, a missing safeguard, or a reused piece of code can cascade into financial ruin, infrastructure chaos, or even fatalities. Humans may write the rules, but computers execute them with relentless precision, often amplifying mistakes far beyond imagination.
Highlighting thorough testing can help readers see how proper safety measures build trust and reduce risks.
Patriot Missile Timing Error Cost Lives
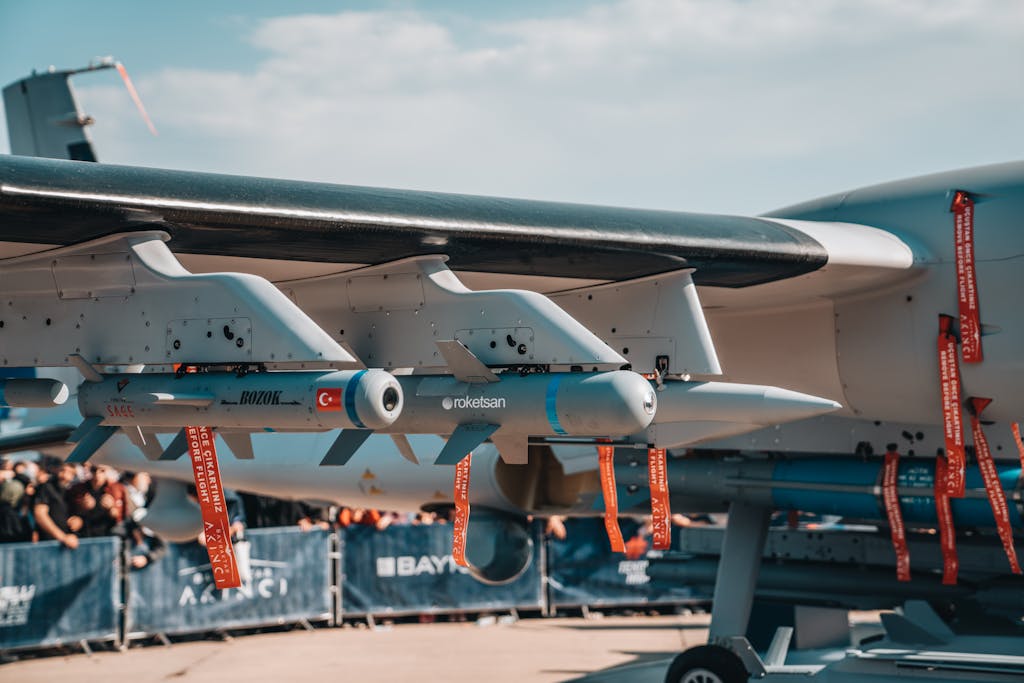
During wartime, a tiny software error quietly escalated into tragedy. The Patriot missile defense system’s internal clock lost precision over long periods of operation.
After more than 100 hours, this minuscule error became significant enough to miscalculate incoming missile trajectories, allowing a Scud to strike a U.S. Army barracks. The result was the death of twenty-eight soldiers and injuries to many more.
What makes this disaster chilling is its subtlety. A fraction of a second error, invisible to most operators, caused catastrophic real-world consequences. It’s a sobering reminder that even the most sophisticated military technology depends on flawless software and careful human oversight.
Computers do exactly what they are told, and a minor programming oversight can quickly turn lethal.
World of Warcraft: Spread a Virtual Plague
Even a game can go horribly wrong. A bug in World of Warcraft allowed a digital disease to spread uncontrollably across crowded in-game cities. Characters died rapidly, players panicked, and some deliberately exploited the glitch, turning the virtual world into chaos.
The event illustrated that software failures are not confined to machines; they interact with human behavior in unpredictable ways. A game bug created a mini-epidemic, demonstrating that even a digital world can become dangerous when errors meet human exploitation.
Software bugs are easy to laugh at when they only crash a browser or a spreadsheet. These seven disasters reveal a darker truth: even a small coding error can escalate into death, destruction, or chaos. Computers execute instructions perfectly, but humans write the rules, and our oversights become magnified in the real world.
Oversight, testing, and humility are never optional when software reaches beyond the screen.
The 2003 Blackout Proved Silent Software Is Deadly
Millions lost power across the U.S. and Canada in one of the largest blackouts in history. Monitoring software failed to alert operators as lines overloaded and cascading failures spread silently.
This highlights the need for rigorous testing and fail-safe design in critical infrastructure to mitigate such risks.
The blackout revealed a frightening truth: silent failures are more dangerous than loud ones.
Critical infrastructure relies on software to warn humans of impending disasters. When alarms fail or remain silent, the consequences ripple across millions of people’s lives, proving that software in essential systems must fail clearly, loudly, and unmistakably.
Sony Rootkit Turned Music Into a Security Trap
Sony BMG installed hidden software on certain music CDs to prevent piracy, but it backfired catastrophically. The program created serious security vulnerabilities, installed itself invisibly on user computers, and hid from antivirus programs.
Customers discovered the hidden software and reacted with outrage, leading to lawsuits, product recalls, and a lasting trust crisis for the company.
This incident showed that software can betray trust as easily as it can protect content. Protective measures that compromise safety or operate in secret create far more danger than the problem they were intended to solve.
Sony’s failure became a case study in why transparency and respect for users must be baked into software design.
Mars Climate Orbiter Lost Over Unit Confusion
The Mars Climate Orbiter mission was supposed to be a milestone in space exploration. Instead, it became a $125 million lesson in precision and communication. One team used English units, while another expected metric units, resulting in incorrect data being fed into trajectory calculations.
The spacecraft drifted far off course and either burned up in the Martian atmosphere or disappeared into space.
This failure underscores how even the smallest miscommunication can lead to catastrophic consequences. Brilliant minds, expensive hardware, and cutting-edge software could not prevent the loss.
It demonstrated that in high-stakes missions, every detail matters, and even small coding or coordination errors can bring an entire project crashing down.
Ariane 5 Rocket Exploded After Reused Code Failed
Ariane 5 was poised to be Europe’s most advanced rocket, but it reused software from an older model, Ariane 4. The new rocket’s flight dynamics differed, and a conversion error triggered a critical failure.
Moments after launch, the rocket veered off course and disintegrated spectacularly, destroying hundreds of millions of dollars’ worth of hardware.
The disaster revealed that old code is not automatically safe in a new environment. Software that worked perfectly yesterday can destroy everything tomorrow if reused without rigorous testing.
Engineers were forced to confront the hard truth: assumptions, shortcuts, or reused programs in high-risk systems are a recipe for catastrophic failure.
Therac-25 Burned Patients to Death

The Therac-25 was designed as a revolutionary cancer treatment machine. It was supposed to save lives, but software flaws turned it into a silent killer. Critical hardware safety features were removed because engineers trusted the computer to handle errors perfectly.
When the system failed, operators saw confusing error messages while patients received massive, sometimes fatal, doses of radiation. Stressing the importance of safety measures can inspire readers to prioritize safety in their own work.
The consequences were horrifying. Patients suffered severe burns, long-term injuries, and death, while the system gave no obvious warning. Hospitals and engineers were forced to confront a terrifying reality: software errors in life-critical machines do not stay confined to code; they become lethal in the real world.
Emphasizing transparency and proper communication can empower readers to advocate for safety and prevent similar tragedies.